AdiRisk – Keeping your ISMS under control
The smart tool for ISO 27001-compliant risk management.
 ISO 27001 ready, with integrated catalogs and SoA-reporting.
 Intuitive & customizable, custom structures, easy to use
 Securely integrated, SSO, AD integration, backup & auditing
Adiccon is an IT and telecommunications consulting firm that supports organizations with networks, information security, and IT projects.
 Founded in 2004 in Darmstadt.
 More than 600 successfully completed projects.
 Approximately 50 employees.
- ISO 27001 certification
Example applicationISMS Tool
What we did
We have developed a flexible ISMS tool that complies with ISO 27001 and critical infrastructure (KRITIS) standards, enables automated risk management, and integrates MFA and SSO. This helps businesses achieve secure and efficient information security.
Project Goal
The goal is the development of a highly adaptable and efficient information security management system (ISMS) that enables dynamic risk management and flexibly responds to individual requirements. The tool meets the requirements of relevant standards such as ISO 27001, BSI catalogs and KRITIS. Security functions such as multi-factor authentication (MFA) and single sign-on (SSO) are seamlessly integrated into the organization's existing IT landscape.
The main functions of AdiRisk
Standard catalogs are customizable
Use integrated measures catalogs for ISO 27001 or B3S and expand them according to your needs. Create your own threats, measures templates and processes.
Roles and users
Starting from the Premium package, different user roles with individual permissions are available. The import of assets and users enables a quick start to the risk process.
Intuitive guidance through the process
The tool guides you through risk management in a logical and simple way. Inventory, categorize, and filter assets flexibly at any time.
Progress tracking
The dashboard displays the progress of the assessment process and the status of your documentation. Use the file repository to directly link your documents
Standards-based
AdiRisk is based on the ISO 27005 risk management standard. Measures catalogs from ISO 27001 and B3S are integrated starting from the Premium package and can be switched flexibly
Tailored to your preferences
Three packages offer scalable solutions for different requirements. The Enterprise version allows for custom color schemes, CI adaptation, and multilingual support.
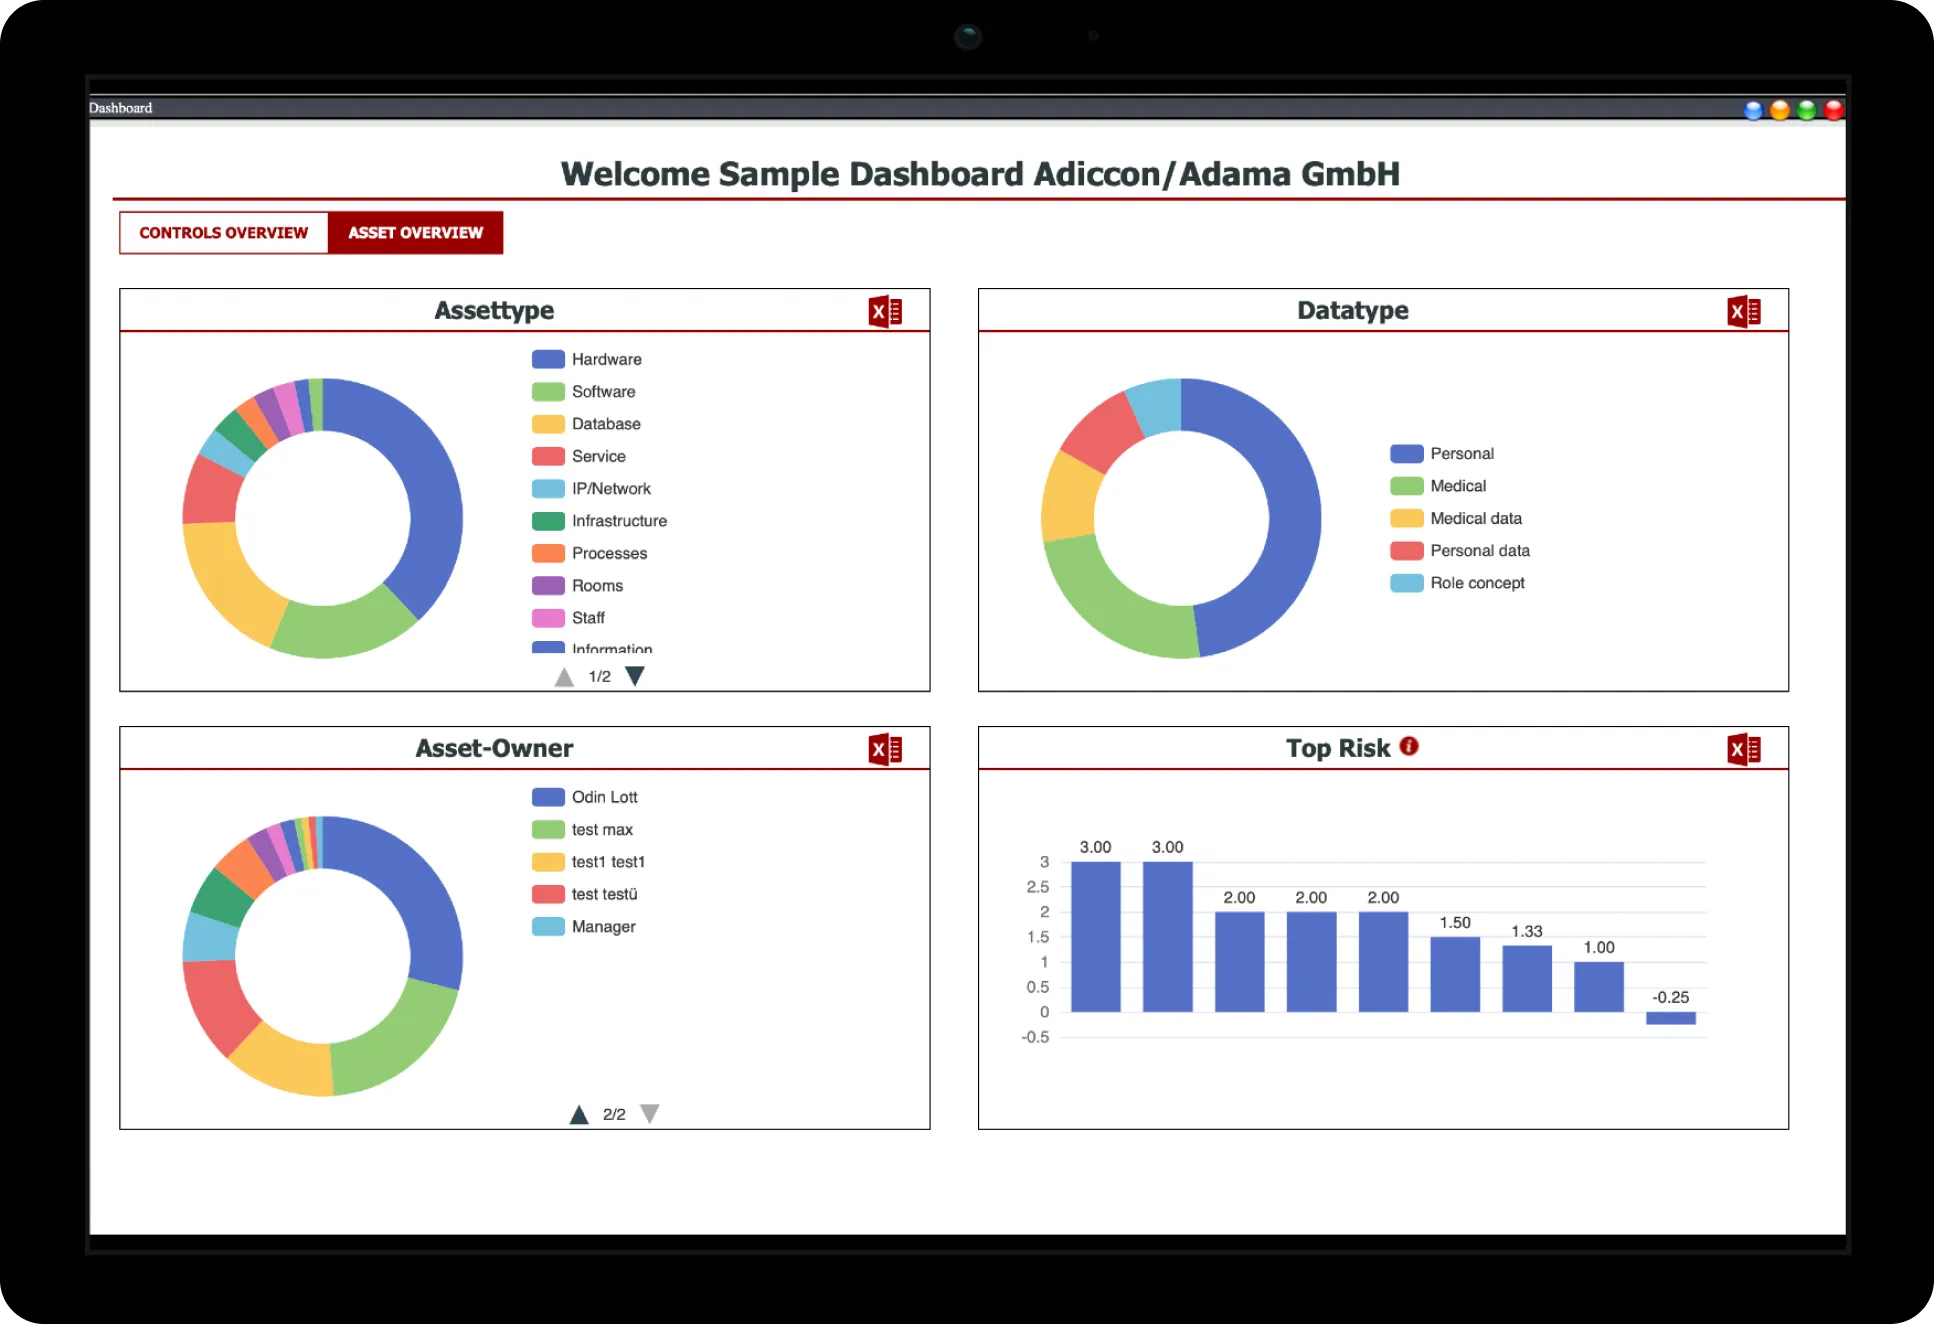
AdiRisk Dashboard
Learn more about AdiRisk; the flexible and intuitive ISMS tool that makes your risk management according to ISO 27001 and other standards simple, secure, and efficient.
Summary of the project
The project has successfully developed a highly customizable and efficient Information Security Management System (ISMS) tool. This tool supports dynamic risk management and effortlessly adapts to individual requirements as well as standards such as ISO 27001, BSI catalogs, and KRITIS standards. It seamlessly integrates security measures like Multi-Factor Authentication (MFA) for login and Single Sign-On (SSO) into the organization’s IT landscape. With its streamlined architecture, the tool enables fast onboarding and is easily adaptable to meet specific needs. Its reliability and efficiency have been proven through successful ISO audits and recertification audits.
“Good risk management has to fit into everyday work. With AdiRisk, ISO 27001 becomes routine instead of a major project.”
Techstack
Programming languages and frameworks
- JavaScript
- Perl
- HTML
- CSS
- Commander-Framework
Security and version control
- SSO
- MFA
- IDP
- Git
Data management and integration
- PostgreSQL
- Integration with ERP/CRM-Systems like SAP

Ready to get started?
Let's talk about your project requirements and together develop a solution that moves your business forward.
Schedule a call